cybersecurity risk

An image of a leader getting executive coaching on digital strategy legal

Executive Coaching on Digital Strategy Legal: A Quiet Power Tool for Justice Leaders

The work you lead is already heavy. Case backlogs. Emergency grants. New reporting rules every year. Now AI tools, cloud systems, and cyber risks sit on top of it all. For legal nonprofits, executive coaching on digital strategy legal is no longer a nice-to-have. It is focused support that helps legal executives, such as the

Executive Coaching on Digital Strategy Legal: A Quiet Power Tool for Justice Leaders Read More »
A team asks the questions what should a board expect to see in a cyber risk report from management

Board Cyber Oversight: What Should a Board Expect To See in a Cyber Risk Report from Management?

You have a board meeting on the calendar. The deck is almost done. But there is one slide that still feels fuzzy: the cyber risk report. Your board now treats cyber exposure the same way it treats financial exposure. Investors, lenders, and regulators see cyber risk as a direct signal of how well the business

Board Cyber Oversight: What Should a Board Expect To See in a Cyber Risk Report from Management? Read More »

A group of leaders discussing the 3 Questions CEOs Must Ask About Security Investments To Protect Growth

3 Questions CEOs Must Ask About Security Investments To Protect Growth

If you feel unsure whether your security budget is too high, too low, or simply misdirected, you are not alone. Most growth-minded CEOs and founders feel the same tension. You sign off on six-figure renewals, sit through vendor pitches, then still worry about the next ransomware headline. Boards, lenders, and large customers now expect clear

3 Questions CEOs Must Ask About Security Investments To Protect Growth Read More »

Why Boards Approve Wrong Security Investments and How to Fix It with CTO Input guidance

Why Boards Approve Wrong Security Investments and How to Fix It with CTO Input guidance

The story is painfully familiar. A mid-market company spends countless dollars on security tools. A breach still hits. Operations stall, customers panic, and the next board meeting turns into a blame session. Everyone around the table thought they were doing the right thing. They approved spend. They bought the big brands. Yet the business was

Why Boards Approve Wrong Security Investments and How to Fix It with CTO Input guidance Read More »

A team discussing cybersecurity requirements for legal aid grantees

Cybersecurity Requirements for Legal Aid Grantees (What Funders Expect in Practice)

It’s 8:12 a.m. A program manager forwards a message that looks like it came from the ED. “Urgent, please review this invoice.” Someone clicked. Now intake is down, staff can’t reach case notes, and the board chair is asking the question nobody wants to answer out loud: Are we meeting our grant cybersecurity requirements? As

Cybersecurity Requirements for Legal Aid Grantees (What Funders Expect in Practice) Read More »

A CEO speaking about legacy system risk to her board boards In plain business terms

How To Talk About Legacy System Risk For Boards In Plain Business Terms

You are a CEO who is spending more on IT infrastructure and getting less back. Every quarter, the slide on “technology risk” gets a little busier, a little more abstract, and a little harder to defend under tough questions from your board. Behind the jargon, your real fear is simple: an old finance platform failing

How To Talk About Legacy System Risk For Boards In Plain Business Terms Read More »

An image of third-party risk management: move from compliance theater to real protection for CEOs

Third-Party Risk Management: Move from compliance theater to real protection for CEOs

You are buried in vendor questionnaires, SOC 2 reports, and security addendums. Your team spends hours chasing signatures and documents. Yet in the back of your mind, you still do not feel safer. That tension is the signal to pay attention to Third-Party Risk Management: From Compliance Theater to Real Protection. Third-party risk management is

Third-Party Risk Management: Move from compliance theater to real protection for CEOs Read More »

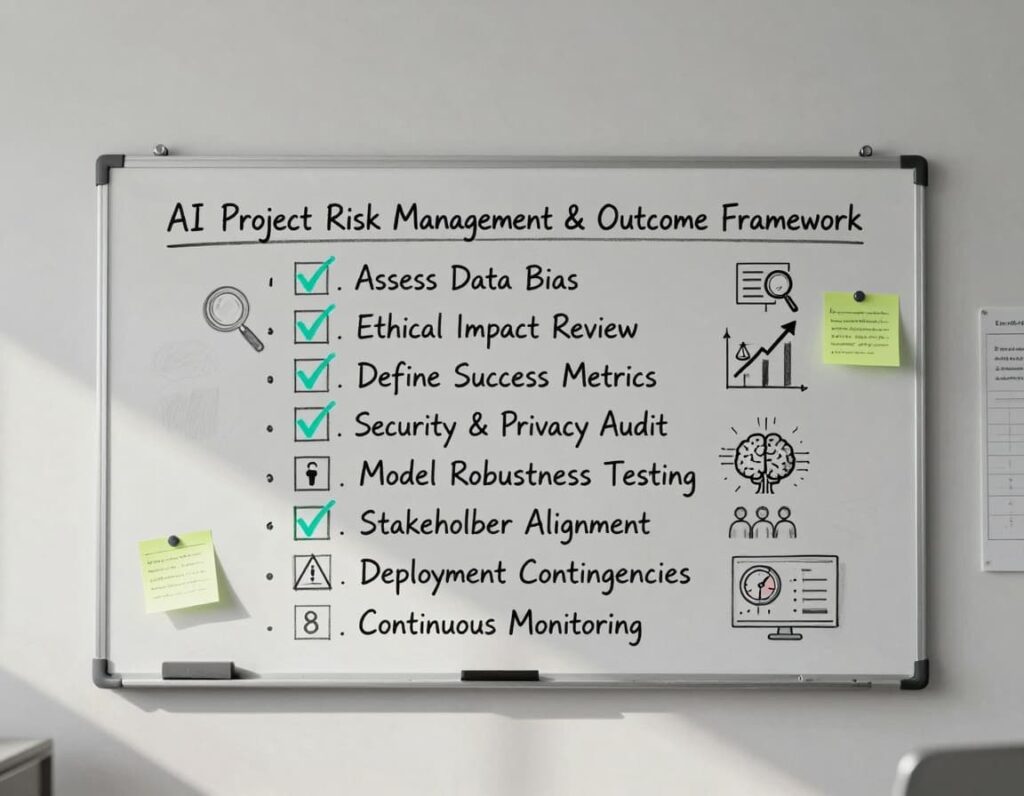
An image of a board checklist for AI projects to manage risk and drive outcomes

Board checklist for AI projects that manages risk and drive business outcomes

You are a CEO, COO, or founder who is spending more on tech and getting less back. Your inbox is full of AI pitches, your team brings slide decks to every planning session, and your board asks, “What is our AI strategy?” while also warning you about risk. You feel the squeeze from every side.

Board checklist for AI projects that manages risk and drive business outcomes Read More »