cybersecurity risk

An image of how fractional CISOs build security programs from zero in 6 months for growth CEOs

How Fractional CISOs Build Security Programs from Zero in 6 Months

You feel the pressure from customers, lenders, and your board. Security questionnaires keep getting longer, regulators are more demanding, and every new breach in the news makes you wonder, “Are we next?” But a full-time CISO is a six-figure hire you cannot justify yet. That is where a fractional CISO fits: an experienced security leader

How Fractional CISOs Build Security Programs from Zero in 6 Months Read More »
A team that is realizing that their vendor risk program is compliance theater and now they want to fix it

Your Vendor Risk Program Is Probably Compliance Theater (And How To Fix It)

Your team spends hours chasing vendor questionnaires, SOC 2 reports, and spreadsheets. Yet when the board asks, “How much risk sits with our key vendors?”, the room goes quiet. That is the gap this article tackles. If Your Vendor Risk Program Is Probably Compliance Theater, it means you are running a security show that looks

Your Vendor Risk Program Is Probably Compliance Theater (And How To Fix It) Read More »

The CEO's Guide to Cyber Risk Assessment in Financial Terms for Mid-Market Growth

The CEO’s Guide to Cyber Risk Assessment in Financial Terms for Mid-Market Growth

If you are a CEO, COO, or founder, you already feel it: technology and cyber risk keep getting more expensive and harder to read. The language is fuzzy, the charts are colorful, and yet no one can tell you in plain numbers what is really at stake. This is where The CEO’s Guide to Cyber

The CEO’s Guide to Cyber Risk Assessment in Financial Terms for Mid-Market Growth Read More »

People taking part in board cyber risk briefings

Board Cyber Risk Briefings For CEOs Who Hate Tech Jargon

Do your eyes glaze over when the “cyber update” slide hits the board deck? You are not alone. Many CEOs and executive directors quietly dread those five minutes. Acronyms, charts, and fear-filled headlines, all wrapped in language that feels closer to an operating manual than a leadership decision. Yet you still sign the contracts, attest

Board Cyber Risk Briefings For CEOs Who Hate Tech Jargon Read More »

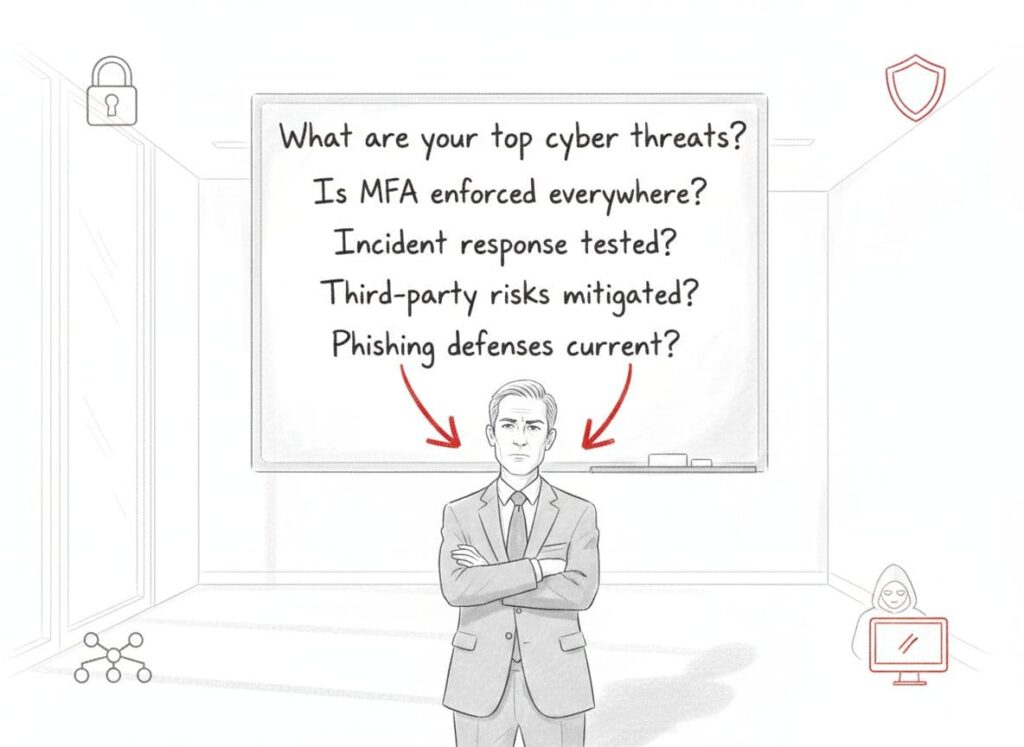
An image of a board questions about ransomware to a CISO

Board Questions About Ransomware Your CISO Should Be Ready To Answer

You are a growth-minded CEO or founder who dreads the moment board members ask, “Are we ready for ransomware?” You feel the tension. Cyber risk goes up every quarter, your technology spend keeps rising, yet you still do not have a story about ransomware readiness that you trust. You get technical answers, not business answers.

Board Questions About Ransomware Your CISO Should Be Ready To Answer Read More »

An image of a board learning about cybersecurity basics for board members

Cybersecurity Basics For Board Members: A Plain Language Guide To Getting It Right

You are a CEO or non-technical board member who keeps hearing, “Cybersecurity is under control.” Then you read about another ransomware story and wonder if your fiduciary duty would make you the one blamed when it hits your company. Regulators, lenders, and customers now expect boards to show real board oversight on cybersecurity basics for

Cybersecurity Basics For Board Members: A Plain Language Guide To Getting It Right Read More »

An image of a board and executive team taking part in a cyber resilience tabletop exercise

How To Test Your Cyber Resilience Before Attackers Do With A Cyber Resilience Tabletop Exercise

You are a growth-minded CEO, COO, or founder who sleeps with one eye on revenue. You are spending more on tech, security tools, and vendors, yet despite these investments in cybersecurity preparedness, you still cannot answer simple board questions like “Could we keep shipping if our core system went down?” “How long before we tell

How To Test Your Cyber Resilience Before Attackers Do With A Cyber Resilience Tabletop Exercise Read More »

An image of a team building a data breach response plan for justice organizations

Building a Data Breach Response Plan for Justice Organizations

A data breach is simple to describe and hard to live through. It involves unauthorized access to information someone should not see, copy, or share. That could be a lost laptop, a compromised email account, or a system quietly siphoning data in the background. For justice organizations, a data breach response plan for justice organizations

Building a Data Breach Response Plan for Justice Organizations Read More »