regulatory compliance

A glowing server hub connects global regions, cloud systems, payment icons, shields, and clocks.

Technology Readiness Checklist for International Expansion

International expansion can expose technology problems that stayed hidden while your business operated in one market. A system that works well at home may not support local privacy rules, new payment methods, regional vendors, or teams working across time zones. A strong technology readiness checklist starts with a pre-expansion assessment of architecture, infrastructure, cybersecurity, and […]

Technology Readiness Checklist for International Expansion Read More »
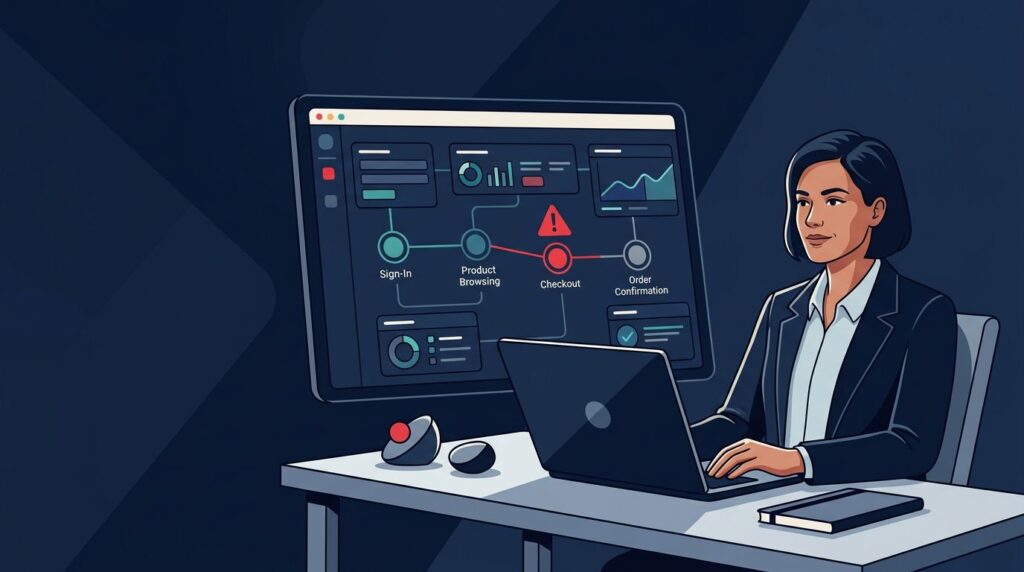
A policy document conflicts with a network dashboard as an executive observes a red warning line.

When an Information Security Policy Becomes a Liability

A written information security policy can look like proof of control until an incident, audit, customer review, or lawsuit tests it against reality. If the document says one thing while your systems, vendors, or employees do another, the policy may give a reviewer a clear record of the gap. That doesn’t create automatic legal liability

When an Information Security Policy Becomes a Liability Read More »

Medical device and laptop linked by secure data lines around a red alert shield.

How to Respond to a Cybersecurity Deficiency Letter

An FDA cybersecurity deficiency letter is not a request for better marketing language. It means the agency cannot verify that your device, software, or postmarket process meets its cybersecurity expectations. Your response must connect each concern to a controlled change, a named owner, and objective evidence. A defensive explanation will not close the gap. A

How to Respond to a Cybersecurity Deficiency Letter Read More »

A glowing workflow network inside a glass shield, connected to approval, privacy, safety, and escalation symbols.

AI Liability Questions to Answer Before Customer Workflow Launch

Customer-facing artificial intelligence systems can answer questions, recommend actions, route cases, approve requests, and shape how people experience your company. That makes AI liability a business issue before it becomes a legal one. A wrong answer, exposed private data, or inconsistent treatment can create safety risks and encourage harmful reliance. Customers won’t blame the model

AI Liability Questions to Answer Before Customer Workflow Launch Read More »

Security leader reviewing a dashboard beside a vault, shield, cloud, and compliance papers.

Fractional CISO for RIAs: SEC Readiness Without a Full-Time Hire

A cyber incident can expose more than client data. It can reveal unclear ownership, weak vendor oversight, and policies that exist only on paper. If you are evaluating a fractional CISO RIA engagement, ask whether an accountable leader can improve your firm’s security posture and turn cyber risk into decisions, evidence, and action. Registered Investment

Fractional CISO for RIAs: SEC Readiness Without a Full-Time Hire Read More »

A glowing cybersecurity shield, secured folders, and a checklist on a desk with network nodes.

CMMC Requirements 2026: A Mid-Year Contract Check

A compliance problem under the Cybersecurity Maturity Model Certification framework rarely starts with a failed assessment. It starts when a bid, flow-down, or renewal lands on your desk and nobody can say what the company has committed to. For defense contractors across the Defense Industrial Base, CMMC requirements 2026 are no longer a future compliance

CMMC Requirements 2026: A Mid-Year Contract Check Read More »