board cyber risk reporting

Robotic factory equipment connects to servers through glowing lines behind a protective shield.

Manufacturing Cybersecurity When OT Meets IT

A ransomware incident at a manufacturer doesn’t stop at an inbox. It can stop a line, delay shipments, compromise product quality, and leave leadership explaining lost margin to customers and the board. That is why cyber risk in the manufacturing sector matters beyond IT. Connected digital technologies turn cyber threats into a business continuity concern,

Manufacturing Cybersecurity When OT Meets IT Read More »
A red alert stands out on a cybersecurity dashboard surrounded by network and protection icons.

Technology Risk Prioritization When Everything Is Urgent

When every technology issue arrives marked urgent, the loudest problem usually gets funded first. Treating every alert as urgent creates alert fatigue and can lead leaders to fund visible but lower-value work. That is how businesses end up patching low-value systems while a critical vendor dependency, recovery gap, or access-control weakness sits open. Technology risk

Technology Risk Prioritization When Everything Is Urgent Read More »

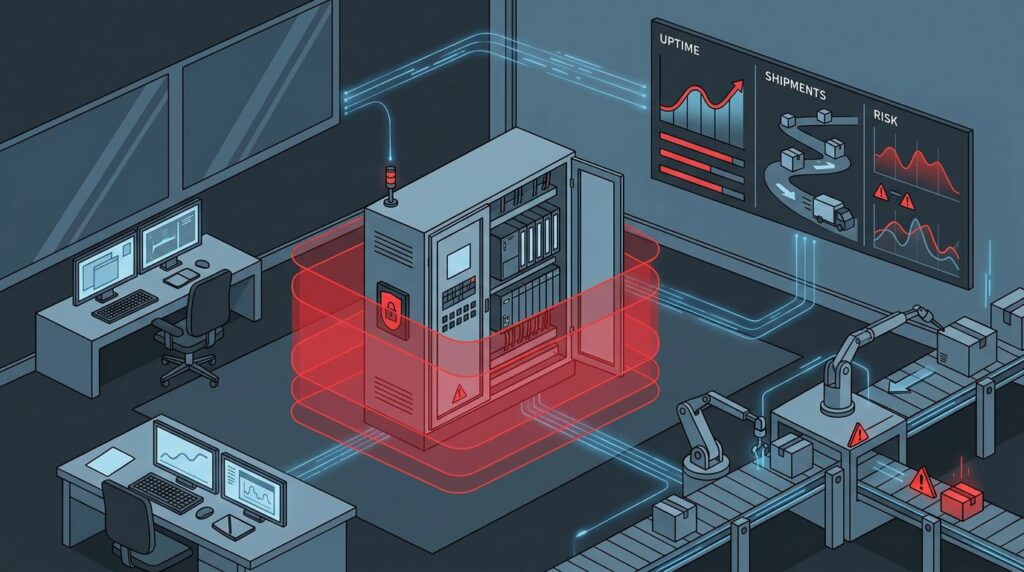
A factory control room with a PLC cabinet protected by glowing red security barriers.

Manufacturing OT Security: Put Plant Risk in Business Terms

A ransomware incident at a manufacturer doesn’t stop at an inbox. It can stop a line, delay shipments, compromise product quality, and leave leaders explaining lost margin to customers and the board. OT security in a plant protects production systems without treating a facility like an office network. It must account for uptime, safety, legacy

Manufacturing OT Security: Put Plant Risk in Business Terms Read More »

A glowing red security shield oversees a structured three-stage cybersecurity roadmap on a dark background.

What a 90-Day Fractional CISO Engagement Produced

A security program can look busy for years and still leave you exposed. Tickets close. Tools renew. Vendors send reports. Then a customer, insurer, buyer, or board member asks a plain question: “What could hurt the business, and who owns the response?” Modern organizations need ongoing cybersecurity leadership to strengthen their overall security posture against

What a 90-Day Fractional CISO Engagement Produced Read More »

When You Need a Public Company CISO

When to Hire Your First Public-Company-Ready CISO (and What to Do Until Then)

You do not need to be listed on an exchange before cyber risk starts acting like a public company problem. The pressure often arrives earlier. A major customer sends a security questionnaire. Your board of directors wants clearer answers. Cyber insurance renewal gets harder. An acquisition is on the horizon. A ransomware event at a

When to Hire Your First Public-Company-Ready CISO (and What to Do Until Then) Read More »