security controls

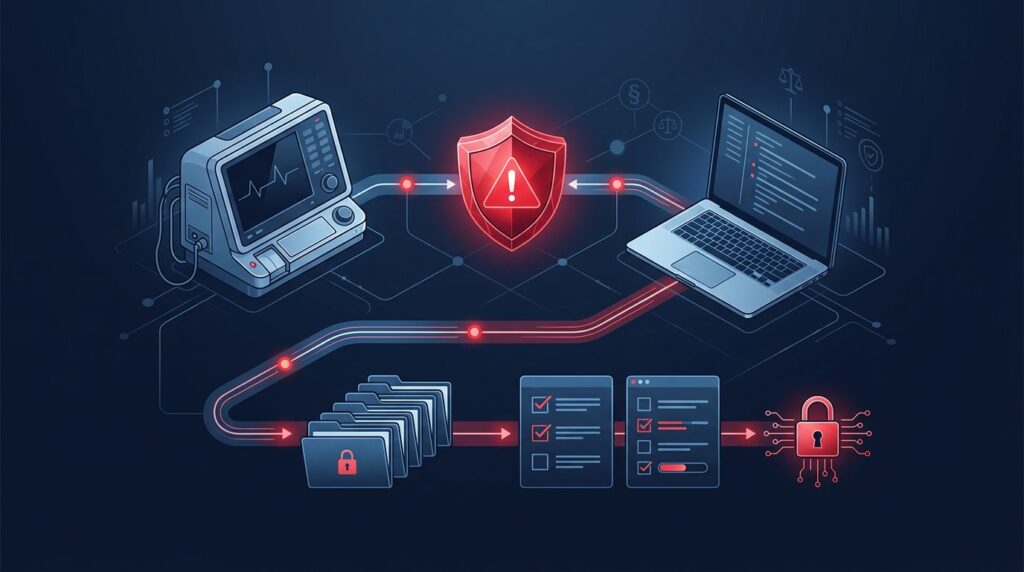
Medical device and laptop linked by secure data lines around a red alert shield.

How to Respond to a Cybersecurity Deficiency Letter

An FDA cybersecurity deficiency letter is not a request for better marketing language. It means the agency cannot verify that your device, software, or postmarket process meets its cybersecurity expectations. Your response must connect each concern to a controlled change, a named owner, and objective evidence. A defensive explanation will not close the gap. A […]

How to Respond to a Cybersecurity Deficiency Letter Read More »
Cyber insurance folder with shield, magnifying glass, checklist, and red risk highlights.

How to Read Your Cyber Insurance Renewal Before Your Broker Does

A cyber insurance renewal can look like routine paperwork until you notice what changed. Higher premiums are only part of the story. The application may now ask whether your security controls are operating across the entire business, not whether someone bought the right tools. You should read the renewal as a review of your cybersecurity

How to Read Your Cyber Insurance Renewal Before Your Broker Does Read More »

A factory control room with a PLC cabinet protected by glowing red security barriers.

Manufacturing OT Security: Put Plant Risk in Business Terms

A ransomware incident at a manufacturer doesn’t stop at an inbox. It can stop a line, delay shipments, compromise product quality, and leave leaders explaining lost margin to customers and the board. OT security in a plant protects production systems without treating a facility like an office network. It must account for uptime, safety, legacy

Manufacturing OT Security: Put Plant Risk in Business Terms Read More »

A glass bridge with stepping stones leads to a glowing doorway across a dark gap.

Rebuild Trust After Breach: A 12-Month Sequence

A breach ends in the incident room long before it ends for customers. They remember what you said, what you withheld, and whether your next promises matched what happened. If you need to rebuild trust after breach, treat trust as an operating obligation, not a public relations campaign. Technical remediation, customer communication, vendor decisions, and

Rebuild Trust After Breach: A 12-Month Sequence Read More »

Pre-IPO Security Maturity: What Institutional Investors Ask in the Roadshow

Pre-IPO Security Maturity: What Institutional Investors Ask in the Roadshow

A roadshow can make a familiar security problem feel much larger. Mastering Pre-IPO Security Maturity is not just a technical requirement but a strategic necessity to prevent deal delays and ensure a successful Initial Public Offering. Institutional investors are not asking whether you have zero cyber risk; they are asking whether you know where risk

Pre-IPO Security Maturity: What Institutional Investors Ask in the Roadshow Read More »

The 30-Day Service Account Register for Justice Nonprofits

A forgotten service account can sit in your systems for years, retaining authentication privileges that let it keep moving data, calling APIs, or giving a vendor quiet access long after the original project ended. That is a real risk for justice nonprofits, because your systems often hold sensitive client, case, and partner data. A simple

The 30-Day Service Account Register for Justice Nonprofits Read More »

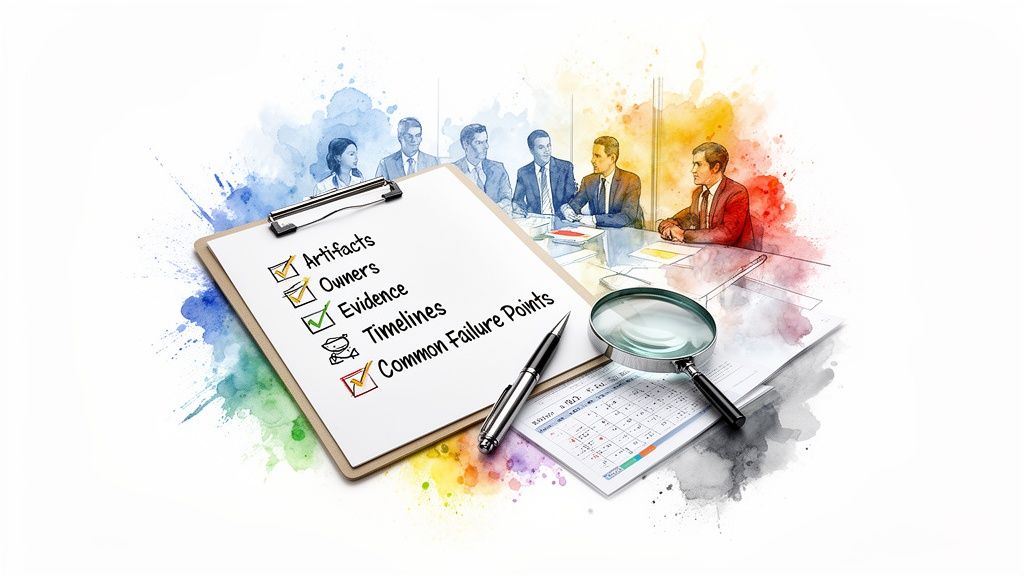
The Board-Ready Audit Readiness Checklist: Beyond the Fire Drill

The annual scramble to prepare for an audit is a symptom of a deeper problem. It’s a recurring fire drill where teams hunt for evidence, rewrite policies, and hope auditors don’t ask the one question nobody can answer. This last-minute chaos isn't just stressful, it's expensive. It drains productive time, delays critical projects, and signals

The Board-Ready Audit Readiness Checklist: Beyond the Fire Drill Read More »